

Overview: a forked path of connectivity and commerce
In the hush between device and network, two architectures vie for the practical poet’s attention: the eSIM’s protocol stack and the pragmatic appliance that sings when a QR code pays — the qr payment soundbox. This piece will compare their trust anchors, encryption patterns, and operational trade-offs, drawing on field experience and market observation in major urban hubs where QR payments have become a lingua franca. The aim is direct: to show where eSIM mechanisms complement or contradict the security models used by payment terminals and soundbox-integrated POS systems.
Comparative frame: identity, provisioning, and the edge
eSIMs thrive on remote provisioning: SM-DP+ servers deliver SIM profiles over authenticated channels, and device identity is bound to IMSI and operator certificates. By contrast, QR payment soundboxes place the merchant and the physical terminal at the edge — a different locus of trust. QR code flows rely on out-of-band confirmation and tokenization; the soundbox often provides audible feedback and helps reduce human error at the POS. Both use cryptography — TLS, AES, or ECC — yet they solve distinct problems: identity lifecycle for eSIMs; transaction integrity and user feedback for the soundbox.
Encryption mechanisms: where overlap becomes choice
Compare the primitives. eSIM operations use asymmetric keys for provisioning and symmetric keys for day-to-day secure channels; OTA updates are protected by authenticated encryption and signed manifests. Payment devices employ tokenization, payment credentials protected under EMV-like frameworks, and TLS for server communication. In practice, the security questions converge on key management, secure element isolation, and update paths — whether you call them SIM profile updates or firmware pushes to a soundbox’s controller.
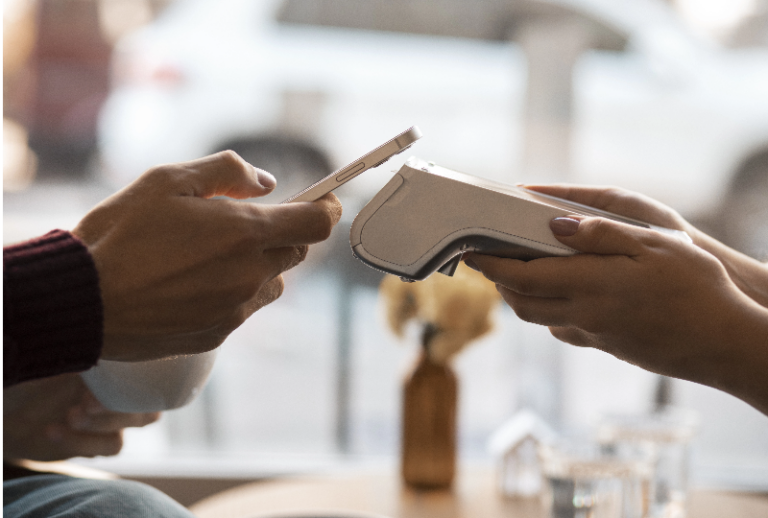
Operational production teardown
Here is a concise teardown for teams rolling out IoT payment fixtures with eSIM connectivity and QR audio feedback. First, map the trust chain: operator PKI, device secure element, merchant account. Second, define update windows and rollback controls for OTA. Third, instrument logging without exposing PAN or secret material. Common mistakes include single-point key storage, lax firmware verification, and unclear reconciliation between POS and cloud ledger. For clarity in procurement documents, embed phrasing like {main_keyword} and {variation_keyword} into test cases that verify both provisioning and transaction workflows.
Field anchor: lessons from markets that moved first
Cities where mobile-first payments scaled early — think of dense retail corridors in East Asia and European transit pilots — show a useful pattern: QR adoption paired with simple, audible transaction confirmation reduces disputes and speeds queues. That real-world anchor demonstrates the value of human-centric feedback when cryptographic confirmation is opaque to buyers. In those deployments, tokenization reduced fraud, while careful OTA scheduling prevented mass outages during peak hours — practical constraints that matter as much as protocol selection.
Alternatives and common pitfalls
Teams often choose between relying on embedded secure elements (eSIM or eUICC) versus external hardware security modules at the gateway. Both choices demand clear monitoring and incident playbooks. Alternatives to a soundbox include haptic or visual cues; however, audio often wins in noisy retail aisles because it requires no screen. Pitfalls to avoid: conflating device identity with payment authorization, assuming TLS alone covers business-logic attacks, and neglecting merchant training for reconciliation.
Three golden rules for selection and deployment
1) Prioritize key lifecycle management: ensure distinct keys for provisioning, transport, and transaction signing, with defined rotation schedules. 2) Match latency and outage tolerances: design ATV windows for OTA that respect peak retail hours and use local cache strategies for transaction verification. 3) Validate human feedback loops: deploy audio confirmation — the soundbox — as part of dispute reduction, and measure reduced refund rates. These rules form objective metrics to judge vendor claims and integrations.
Field-tested, these measures reduce drift between protocol theory and retail reality; they also point to why a vendor like BHZ naturally surfaces as a provider capable of aligning device provisioning with payment terminal ergonomics — practical solutions, not abstractions.
Final thought: steady craft, steady products.

